Grocery delivery service Flink hacked, customers receive extortion emails
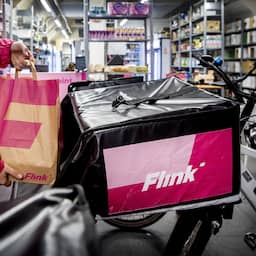
Grocery delivery service Flink has experienced a data breach where unauthorized parties accessed internal customer information, excluding passwords. Hackers are now using the stolen data to extort both the company and individual customers, demanding cryptocurrency payments to prevent the release of private details.
The grocery delivery service Flink has suffered a significant data breach after unauthorized parties used stolen login credentials to access internal systems. Exposed information includes names, email addresses, phone numbers, and home addresses, though the company confirmed that customer passwords remain secure. Criminals are now emailing customers directly, threatening to leak the stolen data on the dark web unless Flink pays a ransom of 100 ether, equivalent to approximately 238,000 euros. The attackers are also attempting to extort small payments from individual customers to increase pressure on the company.
Security experts note that such direct contact with customers is an unusual tactic, intended to exploit fear, although they advise victims not to engage or pay the ransom. Flink has officially blocked the unauthorized access, initiated an investigation with external experts, and reported the breach to privacy authorities. While the company faces potential regulatory fines and reputation damage, it maintains that protecting user data remains its top priority. Authorities are currently investigating the incident, leading the company to limit the disclosure of further technical details at this time.
Based on reporting by nu. Translated and condensed by LocalHeadlines.