Websites of multiple safety regions offline, Amsterdam-Amstelland site remains online
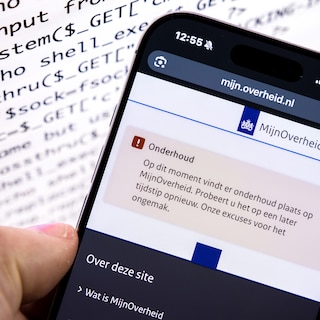
Various websites in the Netherlands, including several regional safety boards and media services, have been taken offline as a precaution due to a high-severity security vulnerability in the PHP programming language. Organizations are following NCSC guidance to disable vulnerable pages while waiting for a fix to prevent potential cyberattacks.
Numerous websites across the Netherlands, including thirteen of the twenty-five regional safety boards, have been taken offline as a precautionary measure due to a critical security vulnerability in the PHP programming language. The National Cyber Security Center (NCSC) issued warnings regarding this flaw, which carries a high risk rating, prompting many organizations to disable their services to prevent potential exploitation by cybercriminals. Notable regional sites affected include those for Zeeland and Rotterdam-Rijnmond, though some, such as Amsterdam-Amstelland, remain functional.
Beyond government entities, the private sector and media organizations have also taken steps to mitigate risks. Streaming service Pathé Thuis and the NPO content upload systems were temporarily deactivated, while the CPNB suspended voting for the NS Publieksprijs. DPG Media has similarly taken several service and brand websites offline, though their primary news portals remain operational. Experts from Cyberveilig Nederland stress that these preemptive closures are necessary given the high severity of the vulnerability, which has also impacted various online platforms internationally in countries like Finland and Belgium.
Based on reporting by parool. Translated and condensed by LocalHeadlines.