Dutch websites unknowingly distributed malicious code that steals data
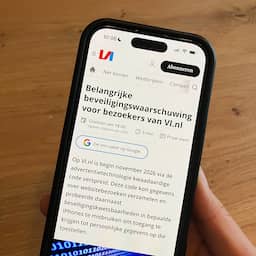
Multiple Dutch websites, including VI.nl and Autoblog.nl, inadvertently distributed malicious code through a compromised advertising system. The code collected visitor data and potentially targeted iPhone users with outdated software, leading sites to urge users to check for security updates.
Several prominent Dutch websites, including VI.nl, Autoblog.nl, and VoetbalPrimeur.nl, have recently spread malicious code through a vulnerability in their shared advertising system. Unauthorized parties accessed the management systems of these platforms, allowing them to inject harmful code into advertisements that collected user data without interaction. The information harvested includes IP addresses, page view history, and device configurations. While officials indicate the vulnerability has now been resolved, the impact remains a point of concern for visitors.
The incident specifically targeted users of certain iPhone models lacking recent security updates, particularly those running older software. Concerned users who visited these websites between November 1 and November 11 are advised to follow security protocols provided on the respective platforms. Although it is currently unclear if sensitive personal information was compromised or if devices were fully breached, administrators are working to mitigate the risks. Affected websites are notifying their user bases and encouraging those with vulnerable hardware to update their systems immediately.
Based on reporting by nu. Translated and condensed by LocalHeadlines.