Websites taken offline as precaution: widely used programming language vulnerable to hacks
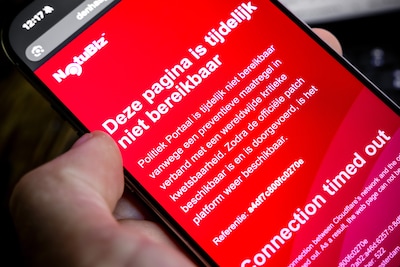
The NotuBiz software provider has proactively taken its websites offline following the discovery of two critical vulnerabilities in the PHP programming language. Security experts urge all affected businesses to install upcoming security patches immediately, as AI-enhanced exploitation tools allow hackers to launch attacks within hours of a vulnerability being disclosed.
The software company NotuBiz has taken its websites offline as a precautionary measure due to two critical vulnerabilities discovered in the PHP programming language. PHP, which powers approximately 70 percent of websites globally including platforms like WordPress, is scheduled to release a security update to address these flaws. Cybersecurity experts warn that these vulnerabilities could allow attackers to gain remote control over servers and access sensitive data.
Experts stress that businesses must install the patch immediately upon its release. The threat landscape has shifted significantly due to the use of AI tools, which now enable cybercriminals to develop exploitation scripts within hours rather than days. Because hackers are expected to actively scan the internet for unpatched systems once the update details are published, companies face a race against time to secure their infrastructure. Authorities and security professionals advise organizations to monitor official channels closely and apply updates the moment they become available to prevent unauthorized access to their servers.
Based on reporting by nu. Translated and condensed by LocalHeadlines.