haarlemsdagblad

Too open and exposed
Too open and exposed

A data breach involving the telecom provider Odido and the hacker group ShinyHunters has resulted in the exposure of user data. The author humorously notes how modern technology now facilitates the public release of private information that people used to accidentally reveal themselves.

Based on reporting by haarlemsdagblad. Translated and condensed by LocalHeadlines.
Related articles

Global online vulnerability update is live: A race against the clock

Global online vulnerability update is live: A race against the clock

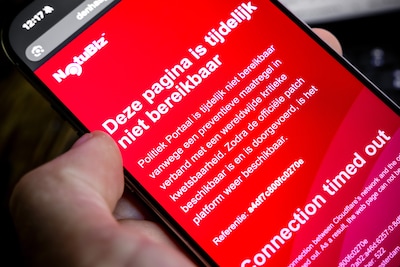
A critical security vulnerability has been discovered in the PHP programming language, prompting a race to patch systems before hackers can exploit the flaw. Many organizations have temporarily taken their websites offline as a precaution while security experts warn that businesses must also conduct thorough checks for prior unauthorized access.

AI-generated texts appear in parliamentary debates: 'Comes at the expense of credibility'

AI-generated texts appear in parliamentary debates: 'Comes at the expense of credibility'

Recent research reveals that 68 members of the Dutch parliament have used artificial intelligence to draft or refine texts for parliamentary debates. While some argue these tools simply aid efficiency, experts warn that over-reliance on AI could compromise the authenticity and public trust of elected officials.

The backbone of the internet is broken: why the attack on PHP is crippling half the web

The backbone of the internet is broken: why the attack on PHP is crippling half the web

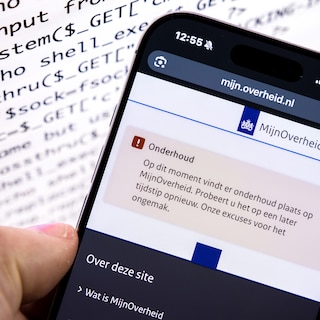
A critical vulnerability in the widely used programming language PHP has forced numerous websites, including government portals, to go offline. Security experts have issued urgent warnings for administrators to install an emergency update to prevent cyberattacks as criminals actively seek to exploit the flaw.

Websites of multiple safety regions offline, Amsterdam-Amstelland site remains online

Websites of multiple safety regions offline, Amsterdam-Amstelland site remains online

Various websites in the Netherlands, including several regional safety boards and media services, have been taken offline as a precaution due to a high-severity security vulnerability in the PHP programming language. Organizations are following NCSC guidance to disable vulnerable pages while waiting for a fix to prevent potential cyberattacks.

European Commission launches investigation into Booking.com over failure to tackle fraud

European Commission launches investigation into Booking.com over failure to tackle fraud

The European Commission has opened an investigation into Booking.com over concerns that the travel platform is failing to adequately combat fraud and phishing scams. The inquiry aims to ensure the company complies with the Digital Services Act, which mandates that online platforms prioritize user protection and transparency.