nu

Lab that was hacked last year allowed to resume contribution to population screening
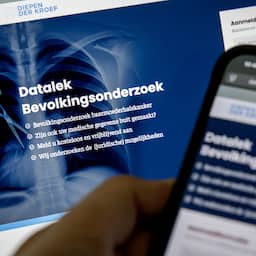
Lab that was hacked last year allowed to resume contribution to population screening

A laboratory responsible for a major data breach has been permitted to resume its role in the national cervical cancer screening program after implementing required security upgrades. Despite this resumption, the facility and the Dutch health ministry are facing a class-action lawsuit from a women's rights group concerned about the ongoing privacy and safety risks caused by the incident.

A medical laboratory that suffered a major data breach last year, resulting in the theft of personal information from 850,000 individuals, has been cleared to resume participation in national cervical cancer screening programs. The breach caused significant processing delays, with wait times for screenings increasing by approximately twenty weeks. Following the incident, the organization Bevolkingsonderzoek Nederland mandated that the lab implement rigorous security upgrades to its IT systems before the partnership could be reinstated. Officials stated that these improvements were essential to ensure both the speed and safety of the national health services provided to women across the country.

Meanwhile, the Women's Right Collective has initiated a class-action claim against the laboratory and the Ministry of Health, Welfare and Sport. The group expresses concerns regarding potential risks to victims, such as stalking or identity fraud, and highlights the danger for women who may be hiding from abusive partners. The organization continues to demand further transparency and financial compensation, noting that they remain dissatisfied with the current information regarding the extent of the security failure.

Based on reporting by nu. Translated and condensed by LocalHeadlines.
Related articles

Several hospitals less accessible due to nationwide KPN outage

Several hospitals less accessible due to nationwide KPN outage

A national KPN network outage caused by a cooling system failure has disrupted telephone services at several hospitals across the Netherlands, including UMC Utrecht and Maastricht UMC+. Affected hospitals are currently utilizing alternative contact numbers to ensure they remain reachable while technical teams work to resolve the widespread connectivity issues.

Albert Heijn parent company files police report following cyber incident: 'Malicious act'

Albert Heijn parent company files police report following cyber incident: 'Malicious act'

The parent company of the Dutch supermarket chain Albert Heijn has filed a formal police report following a cyber incident. The company has officially characterized the event as a malicious act.

Greenwheels and Check to collaborate and double fleet size

Greenwheels and Check to collaborate and double fleet size

Mobility company Pon is integrating its shared vehicle brands Greenwheels and Check to streamline user access and expand its fleet. The companies aim to double their total number of vehicles to twenty thousand by 2030 to encourage shared mobility and reduce reliance on private transport.

Gall & Gall and Etos websites back online, apps remain unreachable

Gall & Gall and Etos websites back online, apps remain unreachable

The websites for Gall & Gall, Etos, and Albert Heijn are back online following a recent cybersecurity incident at Ahold Delhaize, though some app features and delivery services remain restricted. While the investigation into the cause is ongoing, the company has confirmed no current evidence of data theft and normal supply chain operations have resumed.

Number of cybersecurity companies more than quadrupled in five years

Number of cybersecurity companies more than quadrupled in five years

The number of registered cybersecurity companies in the Netherlands has quadrupled since 2021, reaching 962 by October 2024. This rapid growth is driven by increasing cyber threats and regulatory changes, highlighting the ongoing challenge for organizations to protect their digital systems.